Find the affected devices
Can you connect a vulnerable component to a firmware release and the devices running it? An SBOM for your latest build is not enough to identify affected devices running older versions.
Get an independent review of your connected product, with clear recommendations on what to change, what to prioritise, and what can wait.
For manufacturers preparing a new product or supporting devices already in the field.
Talk me through your product and your CRA questions. We’ll work out whether a review would help.
A vulnerable dependency is discovered. You need to know which products are affected, get a fix to them and keep them working. The review looks at what could stop you.
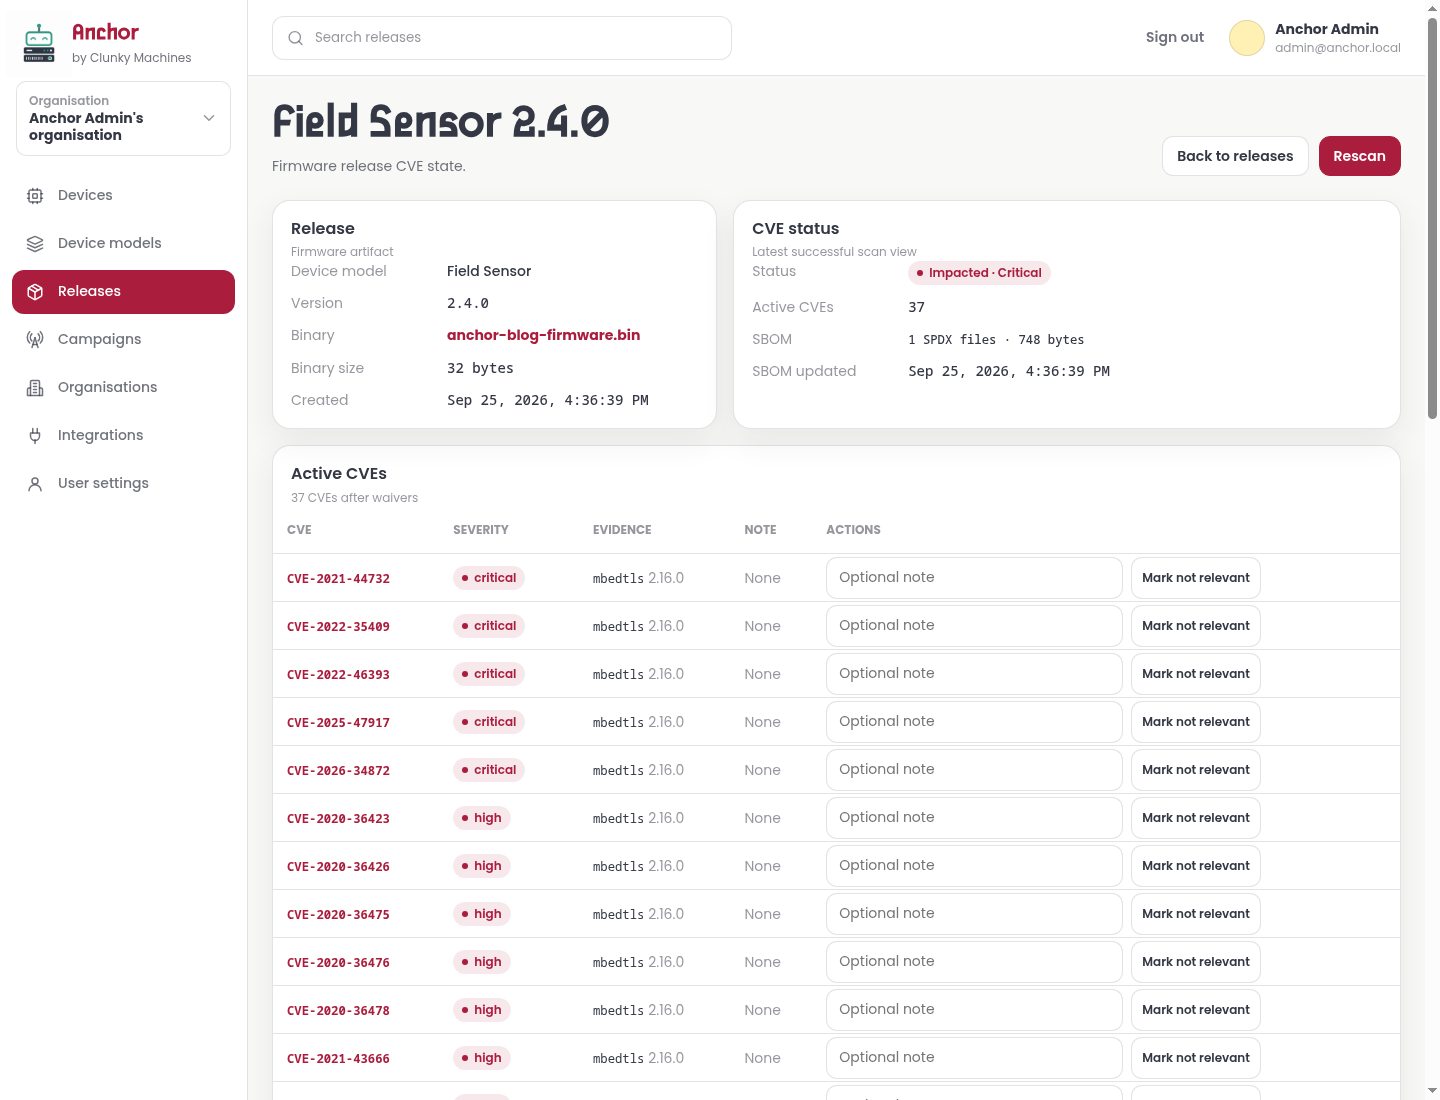
Can you connect a vulnerable component to a firmware release and the devices running it? An SBOM for your latest build is not enough to identify affected devices running older versions.
Can devices reject a tampered image and recover if an update fails? Signing, key storage and recovery need to work together, from the bootloader to the update service.
Can your team assess a vulnerability, ship a correction and track its rollout throughout the support period? This depends on your release process as much as your firmware.
For each gap, understand the product risk, the recommended change and what to tackle first.
We discuss the findings with your team. I can also help implement the changes.
I’m Julien Vermillard. I have 20+ years in software and IoT, including architecture leadership at Sierra Wireless. My work spans device firmware, cloud services and fleet operations.
I contributed LwM2M telemetry scheduling and Fibocom LE250 modem support, both merged into Zephyr. My firmware-update demo also connects Zephyr and MCUboot to remote updates.
View the merged modem support.
View the firmware demoFounder and contributor to Eclipse Leshan, an open-source implementation of LwM2M for device management.
View contributionsI build Anchor, an open-source device management server. This screen connects a release vulnerability scan to the devices reporting that version.
Anchor is in technical preview. Explore the project.
CRA product design, secure updates and vulnerability handling. Announced for , in Labège.
Event announcementCyber Resilience Act session by Julien Vermillard. Announced for .
Programme & speakersDevice management, ownership of the stack and firmware updates, with a Zephyr demonstration.
Talk, slides & demoOctober sessions are listed as announced on 9 October 2026. See the organisers’ pages for current event details.
A review of one product’s architecture and documentation, a written report with prioritised recommendations, and three one-hour remote meetings. We agree the scope and schedule before starting. The price excludes VAT; implementation and deeper testing are scoped separately.
No. This is an engineering review to help you prepare your product. It does not replace a legal assessment, penetration test or formal conformity assessment.
No. I review your existing technology and tooling. Zephyr and Anchor are examples of my engineering work, not prerequisites.
Reporting obligations for actively exploited vulnerabilities and severe security incidents have applied since 11 September 2026. The main obligations apply from 11 December 2027. Check the European Commission overview for the timeline and how the rules apply to your product.
Let’s start with a 30-minute call about your product, your questions and your timeline.